INSIGHTS
French supermarket refrigerators hacked: what the attack on OT systems teaches
On 11–12 October 2026 the refrigeration controllers of hundreds of French supermarkets were taken over remotely and heated to about 50 °C. What is known, why it is a typical OT case, how to protect these systems, which policies respond and why the new product liability directive does not apply.
What happened
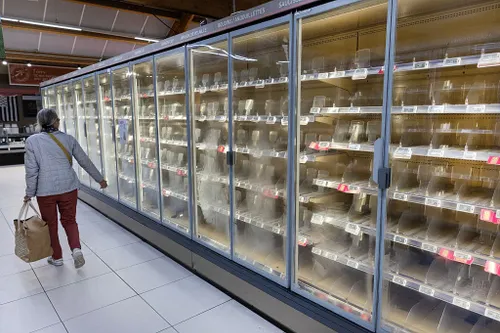
During the night of 11 to 12 October 2026, someone took remote control of the refrigeration systems of hundreds of French supermarkets and triggered forced defrost cycles that heated fridges and freezers to about 50 °C. According to Les Mousquetaires (Intermarché), the heating lasted about six hours. The affected stores had to throw away fresh and frozen products, and the Paris prosecutor's office also mentioned fires (Al Jazeera).
The CEO of Intermarché estimated losses of "tens of millions of euros" in a single day: this is his estimate, not a verified figure.
CERT-FR, the incident response team of the national agency ANSSI, published alert CERTFR-2026-ALE-012 on 12 October (updated on the 13th) on "numerous compromises" of remote refrigeration controllers. The products named are Danfoss AK-SC and AK-SM, and Copeland xweb and Dixell xweb (CERT-FR).
Danfoss stated that most of the affected units are old and no longer receive updates: the AK-SM 800 has been end-of-life since May 2021 and the AK-SC 355 went out of production in 2016. AK-SM 800A units with outdated firmware were also hit (InCyber). According to a source close to the prime minister, ANSSI has been tasked with investigating; the Paris prosecutor's office has opened an inquiry.
What we don't know yet
- Who did it and why. Nobody has claimed the attack. There are no reports of ransom demands or data theft.
- How they got in. Neither the authorities nor Danfoss have named the vulnerability used. Known flaws exist in the AK-SM 800A (CVE-2025-41450, CVE-2025-41451 and CVE-2025-41452, described by Claroty researchers), but nobody has officially linked them to this attack.
- How widespread it is. A Sekoia analyst told Reuters that Spain, Portugal, Poland, Germany and Belgium may also be affected. Retailers in those countries have not confirmed it.
Why it is a typical OT case
OT (operational technology) means the systems that control physical processes: industrial plants, energy, water, refrigeration, buildings. Here no computer was encrypted and no cash register was touched: a physical process was manipulated, and the damage is destroyed goods and, in some cases, fires. Three factors recur in many OT incidents.
- Interfaces reachable from the Internet. According to analyses reported by the trade press, public scans show thousands of management interfaces of these controllers visible online: 2,765 exposed devices according to Censys, cited by Industrial Cyber (Industrial Cyber), and in France 881 hosts according to Censys and 2,898 results according to Shodan (SOCRadar counts, obtained with different methods) (SOCRadar). These are passive scans: they show how much was exposed, not how many devices were compromised.
- Old equipment. A refrigeration plant lasts 15 to 20 years; its software receives no updates for half of that time. CERT-FR warns that an end-of-life device exposed to the Internet, with no fixes available, carries a very high risk of compromise.
- Third-party access. Many retailers do not run these systems themselves: the CEO of Coopérative U explained that his stores buy Danfoss solutions through refrigeration contractors. The risk therefore sits in the supplier chain, often out of sight of whoever suffers the loss.
One more aspect makes these attacks hard to see: defrosting is a normal function. A malicious command can look legitimate if nobody records who issued it.
How to protect an OT environment
Technical measures, in order of priority:
- Know what you have. An inventory of controllers with model, firmware version, location and who accesses them. An external scan of your own public address space is also worthwhile, to find out what is visible.
- No management interface on the Internet. Remote access goes through a VPN or a protected access with multi-factor authentication. Filtering the supplier's IP addresses on a firewall, says CERT-FR, is acceptable only as a temporary measure.
- Govern supplier access. Named accounts, no shared or factory passwords, time-limited and logged sessions, contracts that impose security requirements and the duty to report an incident.
- Separate the networks. The plant network separated from the store network and from the group's IT systems, with a firewall that lets through only the necessary flows. This is the "zones and conduits" idea of the IEC 62443 series of standards.
- Manage updates and end of life. A replacement plan for models no longer supported. Where immediate replacement is not possible, compensate: isolation, access filtering, monitoring. For Danfoss, CERT-FR also recommends setting the "Strict" security level and changing default passwords.
- A second safety layer independent of the network. Temperature alarms with their own sensors and independent notification, and physical limits that no remote command can override. A check that trusts what the controller reports is the same one the attacker manipulates.
- Log and alert. A record of who accesses and what changes, with an alert when defrost schedules or thresholds change.
- Prepare for recovery. Manual procedures to move goods, maintenance contacts, a copy of configurations. Note: a factory reset alone is not enough if the device stays vulnerable and reachable, because it can be compromised again.
How the policy can help, and where it cannot
Everything depends on the policy wording: what follows must be checked against the clauses of each contract.
- Cyber policy. It usually covers incident response costs (forensic, legal and communication consultants), restoration of data and systems, business interruption caused by a cyber event (with a waiting period in hours and a limit) and extortion. Many policies, however, exclude or limit physical damage to property and people, which is exactly the damage of this attack. Check whether the definition of "computer system" includes OT systems and connected devices: often it does so only if it says so expressly.
- Property policy. Spoilage of refrigerated goods is generally covered by an extension tied to accidental breakdown of the plant or power failure. If the cause is a cyber attack, the outcome depends on cyber exclusions and on any clauses that write back cover for fire or explosion. This is the silent cyber issue: the risk is neither clearly included nor clearly excluded. In recent years many insurers have made these wordings explicit.
- Contingent business interruption. It covers the loss of whoever is harmed because a supplier was hit. It often has to be bought as an extension.
- Subrogation. Whoever pays the claim can recover from the party responsible, if there is one: the French press is discussing the liability of refrigeration contractors. That is why it is important to preserve evidence and not to sign waivers or settlements without consulting the insurer.
- War and state-backed attack exclusion. The attack is not attributed. If state involvement emerged, the clauses excluding state-attributed attacks could be invoked: the outcome depends on the wording and on the proof of attribution.
- Care before cutting connections. CERT-FR advises checking insurance conditions before cutting data links with the refrigeration contractor: some maintenance contracts, and some covers, assume remote monitoring.
What to do immediately if hit: notify the broker and the insurer without delay (policies set short notification periods), document everything (temperature logs, photographs, list and value of goods, invoices, communications with suppliers) and preserve the plant logs.
Insurers writing risks with OT systems increasingly ask for an inventory of the plant, network segmentation, multi-factor authentication on remote access, management of end-of-life products and a response plan. After an event like this, those without answers to these questions risk higher premiums, sublimits or OT exclusions at renewal.
Does it fall under the rules starting on 9 December?
The date of 9 December 2026 is that of the new Directive (EU) 2024/2853 on liability for defective products, which replaces the 1985 directive (EUR-Lex). The main novelty: software is a product (Art. 4), including when it is embedded in a device. The manufacturer is therefore liable, without any need to prove fault, for damage caused by a defective product. To assess whether it is defective, account is taken, among other things, of safety requirements, including safety-relevant cybersecurity requirements (Art. 7(2)(f)). According to law firm analyses, failing to provide security updates that the manufacturer could have provided can also make the product defective.
For this case the answer is no, for two reasons.
- Timing. The directive applies to products placed on the market or put into service after 9 December 2026 (Art. 2(1)). The affected controllers were sold years ago and the damage has already occurred: the previous rules and national law apply. Legal analyses point to one exception: a substantial modification of the product after that date can bring it under the new regime.
- Type of damage. The directive compensates death and personal injury, damage to property (excluding property "used exclusively for professional purposes") and the destruction or corruption of data not used for professional purposes (Art. 6(1)). Pure economic loss is not covered. A supermarket's goods are professional property: retailers would therefore have to assert their rights through their contracts with suppliers and national rules, not through this directive.
Where the directive will matter, from 9 December, is for individuals and consumers: a connected device with an unpatched flaw that causes a fire and injures someone is the kind of case it has in mind.
The rule closest to this case is another one: the Cyber Resilience Act, Regulation (EU) 2024/2847 (EUR-Lex). According to the summaries consulted, from 11 September 2026 manufacturers of products with digital elements must report actively exploited vulnerabilities and severe incidents with an early warning within 24 hours and a notification within 72 hours, to the designated national CSIRT, through ENISA's single reporting platform (Art. 14), including for products already on the market (Art. 69(3)). The main obligations, such as security requirements and CE marking, apply from 11 December 2027. If it were established that the attack exploited a vulnerability in a manufacturer's products, that reporting obligation would come into play. As of 13 October, Danfoss had not published any security advisory on this attack.
One last reference: the NIS2 directive includes the production, processing and distribution of food among the sectors concerned. Depending on their activities, some large retail groups may be subject to its obligations on risk management, supply chain security and incident reporting (early warning within 24 hours, notification within 72).
What to do this week
- Look for refrigeration, air conditioning and other plant controllers with a public address and remove the exposure.
- Ask suppliers how they connect, with which credentials and who controls their access.
- Check firmware and end of life of the models, and decide on a replacement plan.
- Install temperature alarms independent of the control system.
- Reread cyber and property policies: definition of computer system, physical damage, refrigerated goods, contingent business interruption, war and state exclusions, notification periods.
FAQ
Is the attack on French supermarkets ransomware?
So far, no. There are no reports of encrypted files or ransom demands: the attackers manipulated refrigeration controllers, forcing defrost cycles that heated fridges and freezers to about 50 °C.
Does a cyber policy cover goods spoiled by an attack like this?
It depends on the wording. Many cyber policies exclude or limit physical damage to property, while spoiled goods are normally covered by a property policy, which in turn may have cyber exclusions. Check the definitions of computer system and cyber event, the exclusions and the sublimits.
Does the product liability directive of 9 December 2026 apply to this attack?
No. It applies to products placed on the market after 9 December 2026 and does not compensate property used exclusively for professional purposes or pure economic loss. The Cyber Resilience Act, with the duty to report exploited vulnerabilities from 11 September 2026, is the rule closest to the case.
Sources
- CERT-FR, alert CERTFR-2026-ALE-012
- The Hacker News, attack on French supermarket refrigerators
- Industrial Cyber, Intermarché and refrigeration risks
- SOCRadar, OT exposure of French supermarkets
- Al Jazeera, "unprecedented" attack on French supermarkets
- InCyber, the obsolescence lead
- Directive (EU) 2024/2853 on liability for defective products
- Cyber Resilience Act, Regulation (EU) 2024/2847
This article is for information only and does not constitute insurance or legal advice. The regulatory summaries are based on third-party analyses and on the official text of the directive: for a specific case, consult a professional.